Private, independent industry initiative. Not a government body.

How we stay transparent

Independent cyber-risk intelligence and access to credible expertise for South African leaders.

Interview · Trade and diplomacy

David Vaverka

“Czech solutions come with a reputation for trustworthiness and no strings attached.”

As Czechia and South Africa close the sixth session of their Joint Committee on Economic Cooperation, the Czech Embassy’s head of economic and commercial affairs in Pretoria on what a deeper partnership looks like past the trade figures — and where cybersecurity fits into it.

Read the interview

Cybersecurity Radar

Everything the radar is tracking.

The headlines above are the surface. Here the full feed is searchable and filterable. Open any item for the complete briefing, which keeps three things apart: the reported fact, our assessment, marked as model inference, and the POPIA or Cybercrimes Act implication.

The Radar supports awareness. It does not predict incidents or replace a professional assessment.

Live feed

Connecting to the Cybersecurity Radar…

How to read an item

Evidence strength

High Primary or official source — vendor advisory, regulator, statement from the affected organisation, CVE record. Named specifics.

Medium Credible reporting citing named sources, but not primary. Details incomplete or second-hand.

Low Single unconfirmed report, anonymous sources, attacker claims, or commentary without original findings.

This rates how well the reported fact is sourced — not how severe the incident is, and not our confidence in the assessment.

How it was checked

Automated Generated by our AI system from the linked report.

Every Radar item carries this badge, because it is true of every item. We do not read the Radar item by item before it is published; we check the ones our rules hold back — an item naming a person in connection with alleged wrongdoing, identifying a private victim, or making a claim that would seriously harm someone if it were wrong. Those are not published until a member of our team has read the source. Nothing on the item says who did that, because a badge on a handful of items would imply a grade of accuracy the others cannot have. Our own writing is in Insights, and it carries a name.

Priority

Priority is reading order for South African leadership — not the severity of the incident. An item becomes Priority 1 through a direct South African link, an effect on critical infrastructure, or an actively exploited vulnerability. A severe global incident with no local link can sit at Priority 2, and a smaller local one can sit at Priority 1.

If you need technical severity, read the reported fact and the original source. We do not publish a severity rating.

The three layers

Reported fact is documented in the source. Assessment is our inference. Recommended next step is a suggestion. They are never merged.
Insights for leaders

Experienced voices. Useful questions. No unnecessary jargon.

The Radar shows what is happening. Insights is where practitioners say what it means — expert interviews and executive briefings that turn a stream of incidents into decisions leadership can act on. Written in business language, by people who have done the work in South Africa, and always naming who is speaking and from what standing.

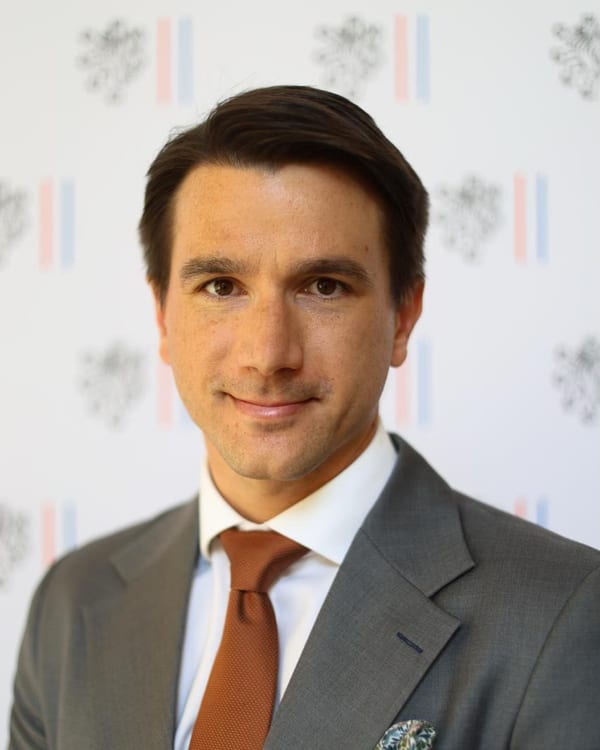
David Vaverka

“Czech solutions come with a reputation for trustworthiness and no strings attached.”

As Czechia and South Africa close the sixth session of their Joint Committee on Economic Cooperation, the Czech Embassy’s head of economic and commercial affairs in Pretoria on what a deeper partnership looks like past the trade figures — and where cybersecurity fits into it.

Read the interview

The South African cyber landscape

We map who appears in South African cyber-risk reporting — automatically, from the reporting itself.

Alongside the Radar, the association is building a living index of the people and organisations that shape cybersecurity in South Africa and beyond — extracted continuously from the same reporting, not compiled by hand.

Figures come from the live index and update on their own. The full index is an internal research tool; what is public here is its shape and size.

Where the risk actually sits

Not every sector carries the same exposure.

Each report is linked to the organisations it names, and those organisations carry a sector. That turns a stream of headlines into a question you can answer: which parts of the South African economy are drawing the most high-priority reporting right now.

11

priority 1 security reports in the last 90 days named Finance & Insurance — more than any other sector, across the 81 organisations we currently track in it

    Sector exposure across the organisations we track, not a measurement of the South African market as a whole. Counts cover the last 90 days — collection started in June 2026, so the window does not yet reach back a full quarter. We count only reports that describe an actual security incident; other coverage of a tracked organisation — results, tariffs, appointments, policy — is excluded even when the organisation is critical infrastructure. Sector is derived from the organisations named in each report; unclassified organisations are excluded. Sectors with few tracked organisations move sharply on a single report. No individual organisation is named on this page.

    Member network

    Cybersecurity companies on CSA.

    Member companies present their services and technology to the business leaders who read CSA, and receive the enquiries that fit them. Membership is a presentation under our Provider Membership Standard — not a certification.

    Membership is not a certification, a guarantee of performance or a regulatory approval. A profile is the company’s own description, except what is marked “Checked by CSA”.

    Looking for help rather than offering it? Find credible expertise

    For cybersecurity providers

    Contribute expertise. Build credible visibility. Meet defined business needs.

    • A company profile on CSA, and the company’s logo in the member list
    • Use of the CSA member mark
    • Invitations to expert interviews and educational contributions
    • Enquiries from businesses, where the company fits the need
    • ZAR 25 000 a year, the same for every member — Provider Membership Standard

    Members

    Barnes Smart Solutions

    Barnes Smart Solutions

    Payment security specialist: secure EMV card data preparation, HSMs and authentication for banks and card issuers.

    Barnes Smart Solutions is an international technology company specialising in payment security. Its flagship P3 platform lets banks, card issuers, card manufacturers and personalisation bureaus prepare EMV card data in-house, with the cryptographic keys behind every card protected by hardware security modules. Barnes also supplies and supports Thales payShield HSMs, instant card issuance, and EMV, NFC and mobile payment testing. It has extended its portfolio into passwordless authentication and security for IoT and edge devices. The company is led by Managing Director Susan Higgo, who is based in South Africa.

    barnessmart.com

    MONET+

    MONET+

    Digital identity and payments software house: passwordless authentication, electronic signatures and payment technology for banks and the public sector.

    MONET+ is a Czech software house that has been building digital identity and payment technology since 1996. Its ProID platform protects employees' digital identities: smart cards and a mobile app provide passwordless multi-factor authentication, qualified electronic signatures and physical access, backed by certificate lifecycle management. MONET+ also supplies the authentication and signing middleware for the Czech electronic ID card, as well as payment technology for banks and transport operators. Its clients include major European banks and public institutions. In South Africa, ProID is delivered and implemented by MONET+'s partner Barnes Smart Solutions. The company is led by CEO Jan Vavrys and is headquartered in Zlín, Czech Republic.

    monetplus.cz

    What we do

    Independent intelligence first. Everything else follows from it.

    The association starts from independent monitoring of the cyber landscape, not a product catalogue — then builds context, understanding and connections around it.

    01

    Continuous cyber intelligence

    Know what is changing.

    Our Cybersecurity Radar monitors global and South African reporting around the clock, triages each development by business priority and turns it into a plain-language summary. It is running live on this page.

    See the Radar

    02

    POPIA & Cybercrimes Act context

    Understand the legal weight.

    Every item on the Radar shows whether — and how — the reported development connects to South African obligations under POPIA and the Cybercrimes Act, so leaders see not only what happened, but what it may mean for them. General information, not legal advice.

    Open any Radar item

    03

    Independent expertise & network

    Reach the right people.

    We connect defined business needs with cybersecurity companies presented on our platform under our Provider Membership Standard, and with experienced practitioners — locally and internationally.

    About the network

    Trust & independence

    Trust requires transparency.

    Cybersecurity Association South Africa is a privately operated, independent industry platform run by bodhi.style s.r.o., a Czech company. We are not part of, endorsed by or affiliated with the South African Government, a regulator, law-enforcement agency or any public authority, unless a specific collaboration is expressly stated. We are not an association or professional body; membership is a contractual programme. Membership and sponsorship do not buy editorial treatment. We disclose material relationships — including those of companies connected with the people who run CSA — and label AI-generated content.

    The Embassy of the Czech Republic in Pretoria has expressed its general support for CSA’s mission in a letter dated 15 October 2026, and we show this as “Supported by the Embassy of the Czech Republic in Pretoria”. That support is not funding, it is not an endorsement of individual content, member companies or providers, and it gives the Embassy no say in what we publish.

    Members pay a membership fee, and companies connected with the people who run CSA may do business with member companies. These relationships are disclosed where relevant. They do not purchase favourable editorial conclusions.

    Information published on this site is for general educational purposes. It is not legal advice, regulatory approval or a substitute for an assessment of an organisation's specific circumstances.

    A practical starting point

    You do not need to become a cybersecurity expert. You need to know which questions to ask.

    Cyber risk can interrupt operations, expose personal information and damage trust. We make the subject manageable, so leadership teams can focus attention and investment where they matter most.

    1. 01What could stop our business from operating?
    2. 02Which information would cause the greatest harm if exposed?
    3. 03Do we know who is responsible when an incident occurs?

    Where to start

    Cybersecurity becomes manageable when the next step is clear.

    Even if the question is not yet fully formed.

    Find credible expertise

    Confidential. Practical. No technical preparation required.