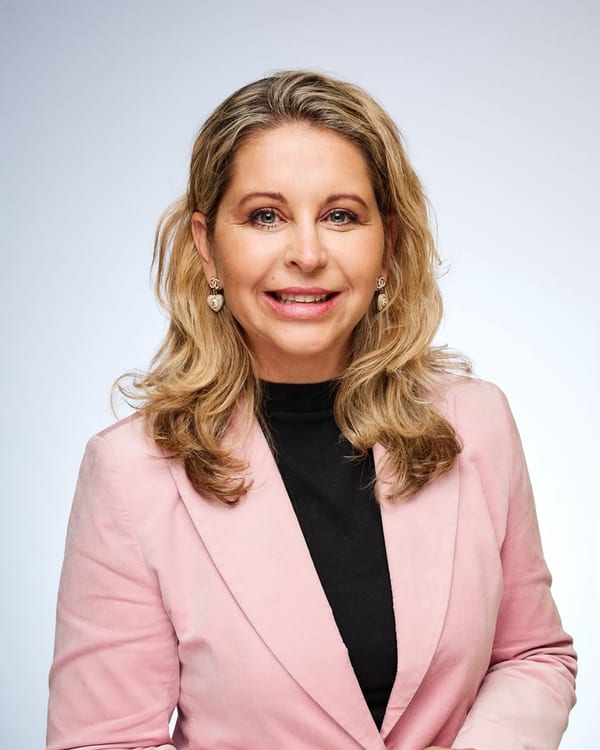
Our guest today is Susan Higgo, Managing Director of Barnes Smart Solutions. Head office in London with the South African office in Stellenbosch. Barnes Smart Solutions’ offering spans from the company's established P3 platform for secure EMV card data preparation, utilised by Banks and cardbureaus world wideand its newer offerings in passwordless multifactor authentication and edge AI. Susanbrings a practical business view to a central cybersecurity question: how can organisations protect trust when attackers increasingly target people, credentials and approval processes, not only the infrastructure behind a transaction? Susan, welcome to CSA Insights.
Getting to know you
Susan, you lead a company whose work spans payments, cryptography and digital identityand edge AI. What have you learned about cybersecurity from the business side that you would never have understood by looking at it purely as a technical problem?
The business lesson is that security control has to work under real operating pressure. A technically sound system can still fail if an employee shares a login to keep a queue moving, a help desk bypasses verification, or someone approves an urgent paymentbecause they believe the instruction came from the managing director.
I therefore start with the business process: who needs access, what are they allowed to do, and what happens when something goes wrong. In a South African hospital, for example, access must be quick enough for a clinician to do their job, while still identifying the individual using a shared workstation. In a finance department, a secure login must be accompanied by proper controls over supplier changes and payments.
That is the context in which we position ProID, developed by MONET+. Its smart card and mobile authentication options can help organisations strengthen workforce access without making every employee remember more passwords. The implementation still needs clear ownership, usable enrolment and recovery procedures, and training. I would measure success through reliable access, fewer avoidable support calls and a demonstrable reduction in exposure, rather than simply counting licences installed.
When attackers target people
SABRIC's annual crime statistics for 2025 put reported digital banking losses at around R2.4 billion. Perhaps more telling than the number is the pattern behind it: criminals increasingly appear to exploit people, credentials and authentication processes rather than break directly into banking systems. Has the weakest point in financial security effectively moved from the infrastructure to the identity of the person using it?
For many digital fraud scenarios, identity and approval processes have become particularly attractive targets. I would be careful about calling the customer or employee the weakest link, though. Criminals exploit the trust and processes around that person,and those processes are something organisations can improve.
SABRIC's 2025 report describes digital banking crime driven largely by social engineering and customer compromise or manipulation. An attacker may persuade someone to disclose credentials, install remote access software or authorise a payment. The banking infrastructure can then carry out an instruction that appears legitimate. That means we have to protect how trust is established and how it is used, as well as the infrastructure itself.
For enterprises, that includes securing employee and administrator access, controlling which devices and credentials can be registered, and acting quickly when access is compromised. ProID's role is particularly relevant to workforce access, including computers, VPNs and business applications. Banks also need transaction monitoring, fraud controls and secure customer recovery processes. Strong authentication can reduce important routes into an organisation, but its effectiveness depends on the surrounding controls and the particular authentication method deployed.
SABRIC also reported a sharp rise in account-takeover fraud during 2025. If criminals can persuade a legitimate customer to reveal credentials or approve an action themselves, what should banks and enterprises be doing differently to tell a legitimate user apart from a manipulated legitimate user?
Authenticating a person does not tell you whether they understand what they are being asked to approve. A genuine customer can use their own device and still be acting under a criminal's instructions. Banks therefore need to assess the proposed action and its context alongside the login.
I would look closely at combinations such as a newly registered device, a new beneficiary and an unusually large payment. Higher-risk actions should trigger additional verification or review, and the customer should see clear details of the recipient and amount. Where the banking system supports it, cryptographically binding an approval to those specific details can help prevent an approved instruction from being substituted. Even then, a customer can be deceived about a genuine payment, so fraud monitoringand intervention remain necessary.
The enterprise equivalent is a finance employee receiving a convincing request to change a supplier's bank details. We should verify the change through an independently established contact and require appropriate separate approval. ProID can strengthen theemployee's authentication into the relevant system; the business application must enforce authority and approval rules. We should test those controls together, rather than assume a successful MFA challenge proves that a payment is safe.
Beyond passwords and what AI changes
Phishing-resistant, passwordless authentication is often presented as the answer to stolen passwords and intercepted one-time PINs, and Barnes offers ProID, developed by MONET+, in this space. But removing the password does not remove the attacker. Where does the attack move next —device enrolment, identity proofing, account recovery, help desks? And how do you stop passwordless security from simply relocating the weakest link?
Attackers will look for the easiest remaining route, which can include registering their own device, impersonating a user to the help desk, abusing account recovery or stealing an already authenticated session. The whole credential lifecycle needs to be designed and tested.
Enrolment should establish the person's identity before granting access, and adding another authenticator should require appropriate verification. Help desk staff need defined procedures that an urgent caller cannot override. Lost devices and cards must bereported and revoked promptly, with affected sessions addressed as well. Recovery should restore access at an assurance level appropriate to the account, supported by notifications and an audit trail. For sensitive roles, I would provide a securely enrolled backup credential rather than allow a convenient fallback to undermine the main control.[7]
With ProID, we can select smart card, mobile and other supported authentication options to suit the environment. But passwordless and phishing-resistant are different claims. FIDO2/WebAuthn and appropriately configured certificate-based protocols can provide phishing resistance; ordinary OTPs or a basic approval prompt do not automatically provide it. We need to verify the actual protocol, application integration and fallback path. I would include simulated enrolment and recovery attacks in the acceptance testing, alongside checks on device security and session handling.
In its African Cyberthreat Assessment Report 2026, INTERPOL estimates that artificial intelligence is enabling more than half of reported cybercrime across Africa. Is AI fundamentally changing the economics of cybercrime by allowing relatively unsophisticated criminals to launch sophisticated attacks at industrial scale —and what does that mean for defenders?
Yes. AI lowers the effort needed to produce convincing messages and impersonations, and allows criminals to repeat and adapt them at scale. INTERPOL's 2026 assessment links AI to 55 per cent of reported cybercrime across Africa. That is a finding about reported activity, but it reinforces the need to prepare for more credible deception.
For South African businesses, I would be concerned about a finance team receiving a convincing supplier email or an instruction that appears to come from an executive. Staff should be supported by a process that requires independent verification, even whenthe message sounds familiar and the request is urgent. Recognising poor spelling or an unusual voice is no longer a sufficient control.
The response is to make successful fraud require more than a persuasive story. Strong authentication, tightly controlled credential recovery and separate approval for sensitive actions can raise the effort required. This is where ProID can contribute to workforce security, alongside endpoint protection and business controls. Defenders can also use automation and AI to help investigate suspicious activity, but those tools need oversight and sound data. I would invest first in controls that continue to work when a convincing impersonation reaches an employee.
South African digital identity and regulation
South Africa is working towards a digital ID built around a mobile credential, remote verification and biometrics. Done well, it could dramatically reduce identity friction and fraud. Done badly, it could create one of the most valuable identity targetsin the country. From a security architecture perspective, what separates those two outcomes?
The difference lies in the trust model and governance across the entire lifecycle. A digital credential should give a service reliable evidence about a person while exposing only the information needed for that interaction. Home Affairs' proposed frameworkenvisages mobile credentials and remote biometric verification alongside physical identity documents, which makes both security and inclusion central design questions.
I would separate initial identity proofing from subsequent authentication. Enrolment needs checks against authoritative records, resistance to biometric spoofing and a route for handling errors. The credential must then be protected cryptographically, withappropriate key protection, expiry, revocation and secure transfer to a replacement device. A biometric match alone should not grant unrestricted authority to every service. Each service still needs to decide what the verified person is permitted to do.
Privacy must be built into the architecture. A service should not routinely receive a copy of someone's entire identity record or raw biometric data. We also need independent security testing, controlled administrator access and a tested response to compromised credentials or infrastructure. People without suitable smartphones, and those who cannot complete biometric checks, need a safe alternative. The same principles inform how we approach workplace authentication with ProID: establish identity properly, control the credential and make recovery trustworthy.
The Joint Standard on Cybersecurity and Cyber Resilience has applied to South African financial institutions since June 2025. Are you seeing it materially change the way they buy and design security —or is there still a danger that cyber resilience becomes a compliance exercise rather than an engineering discipline?
There is evidence that the standard is influencing governance. One of the big 5 banks in SAspublished 2025 governance report, for example, records a self-assessment against Joint Standard 2 of 2024 ahead of its effective date. That is a useful indication of institutional attention, although a self-assessment does not by itself demonstrate how controls perform during an attack.
The standard took effect on 1 June 2025 and creates concrete obligations for the financial institutions within its scope. These include identity and access management, MFA for access to critical system functions and sensitive internet-facing applications, as well as detection, response, recovery and testing. It gives boards a stronger basis for asking how cyber risk is actually being controlled.
For a ProID project, I would turn the requirements into practical acceptance criteria: verify coverage of the intended users and applications, test enrolment and lost-device recovery, confirm that access can be revoked, and establish how events reach the institution's monitoring process. The wider programme must also address privileged access, access reviews, suppliers and service recovery. My concern would be procurement that accepts a feature list without testing the deployed environment. Cyber resiliencebecomes an engineering discipline when the institution can show what happens during a realistic failure or attack, and can demonstrate that identified gaps were fixed.
Barnes and the African market
Barnes works with banks, card issuers and other organisations in Africa as well as internationally. What have you learned from African customers that challenges the assumptions security vendors make when they design products primarily for European or North American markets?
The assumption I would challenge is that every employee has the same devices, connectivity and working environment. South Africa has sophisticated financial and technology infrastructure, but a bank's head office, a hospital ward and a remote industrial site can have very different needs. Africa also comprises distinct markets with different regulatory and operating conditions.
A design that assumes everyone uses a personal smartphone, has continuous internet access or works only in modern cloud applications can exclude users or leave important systems unprotected. We need to accommodate shared workstations, contractors and existing infrastructure. Any requirement to operate during an outage must be tested for the particular use case; installing a system on premises does not automatically make every authentication flow work offline.
That is why ProID's combination of smart card and mobile options, and the availability of SaaS or on-premises deployment, are relevant. The choice should follow the customer's users, architecture and support capacity. South African buyers should also understand where identity data and keys are handled, who can administer them, and the full implementation and support cost. POPIA sets conditions for protecting and transferring personal information; local hosting alone is not proof of compliance. Local partners can help with integration, training and ongoing support, which should be part of the design from the outset.
Barnes built its position around P3 and highly controlled EMV data preparation, where keys, cryptography and issuance processes operate inside tightly defined trust boundaries. You are now expanding further into digital identity and access management. Are payments and identity ultimately becoming the same security problem: deciding who or what should be trusted at the moment a transaction or action is authorised?
They share a central question about trust, but they address different parts of the process. In payments, we need confidence in the credential, the cryptographic material and the authorised transaction. In workforce identity, we need confidence in the person or device requesting access and in the authority attached to that identity.
P3 prepares EMV card personalisation data and supports control over the cryptographic material used in issuance. ProID focuses on workforce credentials and authentication. The connection is practical: the person operating an issuance environment also needsappropriately controlled access. Strong card cryptography and strong operator authentication protect different points in the same chain of trust.
The discipline carries across both areas: protect keys, define who can issue or change credentials, record sensitive actions and revoke trust when circumstances change. Similar questions arise for applications and devices using digital certificates. We should still be precise about scope. EMV data preparation does not replace a bank's fraud controls, and workforce MFA does not provide a complete identity governance programme. For South African organisations, the opportunity is to connect these controls so that a sensitive action has a clear, auditable path from identity to authority to execution.
Practical advice and looking ahead
If you were advising a CEO with a limited cybersecurity budget, who is looking for a workforce security solution, what would be the first three areas you would secure —and why those three?
First, I would secure the identities that open the most valuable doors: email, remote access, administrator accounts and the people who control payments or sensitive data. Use strong MFA, give people individual accounts, remove unnecessary privileges and withdraw access promptly when someone leaves. ProID may be useful where the organisation needs stronger authentication across computers and business systems. Start by understanding existing controls and the gaps.
Second, I would protect the processes that move money. Supplier bank-detail changes, payroll changes and significant payments need defined approval limits, independent verification and separation of duties. A rushed instruction from an executive should still follow the agreed process. These controls can be inexpensive compared with the loss they prevent.
Third, I would secure and prove recovery of the systems the business cannot operate without. That includes supported and patched systems, endpoint protection, backups protected from ordinary administrator compromise, and restore tests. Someone must own theincident response process and know how to isolate affected systems and contact the right people.
I would phase the work around the highest risks and measure whether it actually improves protection and continuity. A limited budget makes prioritisation and reliable implementation more important than buying a long list of features.
Imagine South Africa five years from now. What single change in identity, authentication or payment security would convince you that we had genuinely made cybercrime harder —rather than simply spending more money on cybersecurity?
By 2031, the change I would want to see is a trustworthy identity lifecycle becoming normal across banking, government services and workplaces. A stolen password or an easily intercepted code should no longer be enough to take over a valuable account, and a fraudster should not be able to bypass stronger authentication by manipulating enrolment or recovery.
I would look for evidence in outcomes: a sustained fall in account-takeover losses relative to transaction volumes, fewer successful fraudulent credential resets, and rapid revocation when a device or credential is compromised. We should report scams involving manipulated, authorised payments separately, because even strong authentication cannot guarantee that the person understands the criminal's deception. Those losses need their own prevention measures.
For ProID and similar workforce solutions, the contribution would be reliable strong authentication in everyday systems, backed by secure administration and recovery. The national measure of success must also include accessibility: people should be able touse essential services safely without needing expensive devices or being locked out by a failed biometric check. I would be convinced by criminals finding account takeover harder in practice while legitimate users retain dependable access to their money, work and services.